CoursesBackend engineering from first request to production
Puzzle 10 · 11 of 18
Who vouched for the caller?
Follow a session from an identity check to permission on one row.
All puzzles in this course
The problem
Ada can read river before lunch. After the session expires she asks for the same row. What changed if the database row is identical?
See it
Scroll sideways to see the full diagram.
Find the synthetic session.
Step 1 of 4Check the current time against its expiry.
Step 2 of 4Compare the verified identity with the resource.
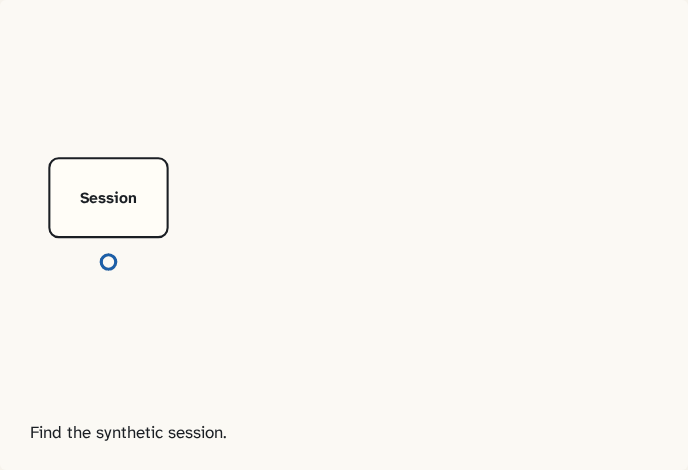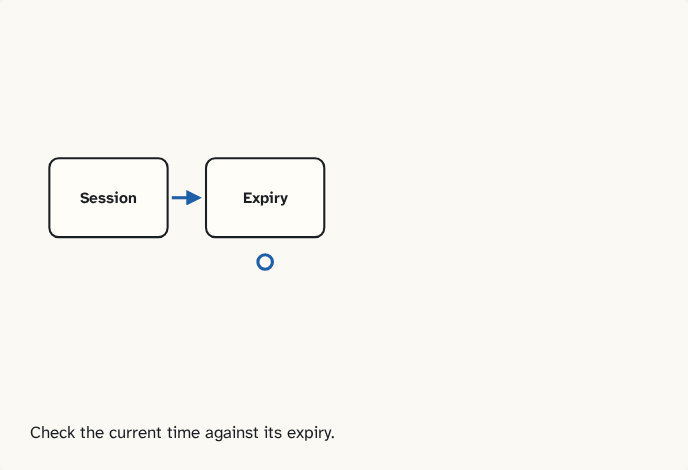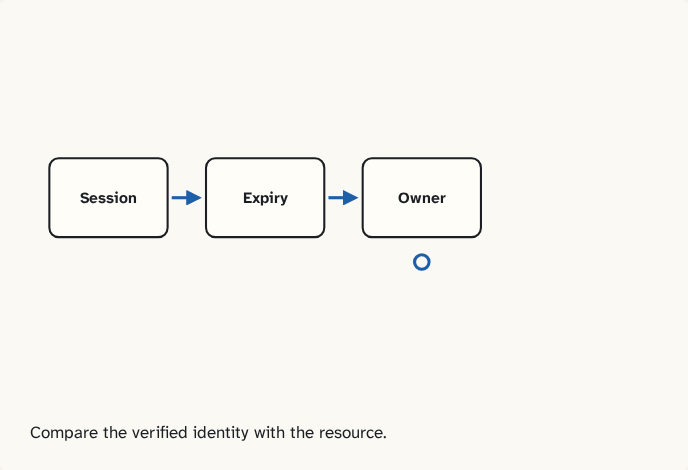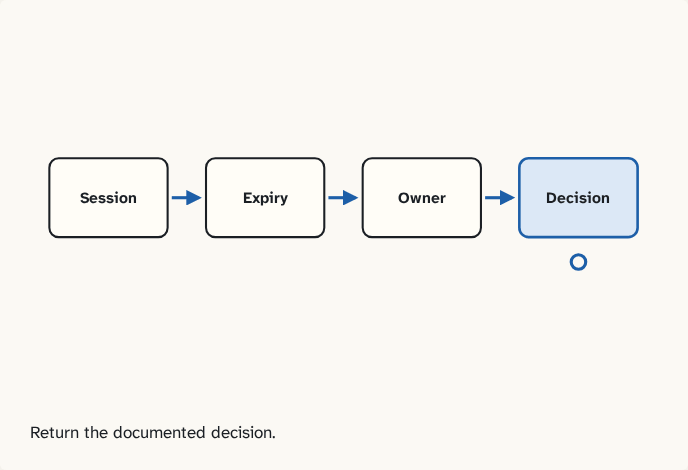
Step 3 of 4Return the documented decision.
Step 4 of 4
The building block
After a successful sign-in, a service may issue a session identifier and keep its owner and expiry on the server. On each protected route it checks the session and then the permission for the resource. The workbench starts with invented session records. An unknown or expired record yields 401. In this exercise a known user without permission gets 403. A real login also needs secure credential handling, protected transport and a revocation policy. Use an established identity provider when implementing the portfolio version.
Place requests on the expiry boundary
In the model a session belongs to Ada and is valid while the server's current tick is strictly below 100. At 99 the lookup succeeds and her own bookmark is visible. At 100 it fails even if the record has not been physically removed. Revocation handles an earlier cutoff: deleting the record at 98 means a request arriving at 99 also fails. This separates how long a credential was originally issued for from whether the server still accepts it now.
Try it
Optional local lab
Freeze time one tick before expiry and then exactly at expiry. Revoke a fixture and show that a subsequent request requires authentication.
Check yourself
Sources
What you now know
Session expiry and resource ownership answer different questions.
Answer every question above correctly to unlock the next puzzle.
Something wrong or unclear on this page? Tell me: a puzzle that didn't click is a bug in the puzzle.