Encryption, from the ground up · Puzzle 8 · 9 of 9
TLS, the blocks together
Puzzles 0 to 7 each stopped one thing a machine in the middle could do. The S in HTTPS is those blocks put together in one short conversation before your first request.
The problem
Puzzle 0 named three things a machine in the middle can do: read, change, pretend. Puzzles 1 to 7 each built one block: symmetric encryption, key exchange, hashes, signatures and certificates. Your app opens an https address and sends a request a moment later. How do all those blocks fit into that moment?
See it
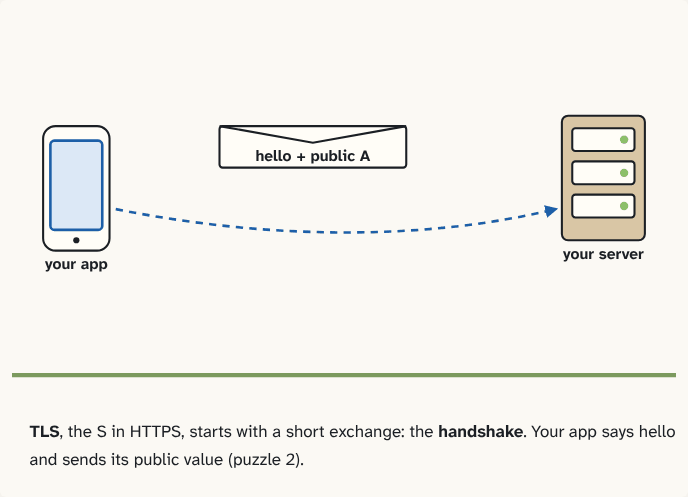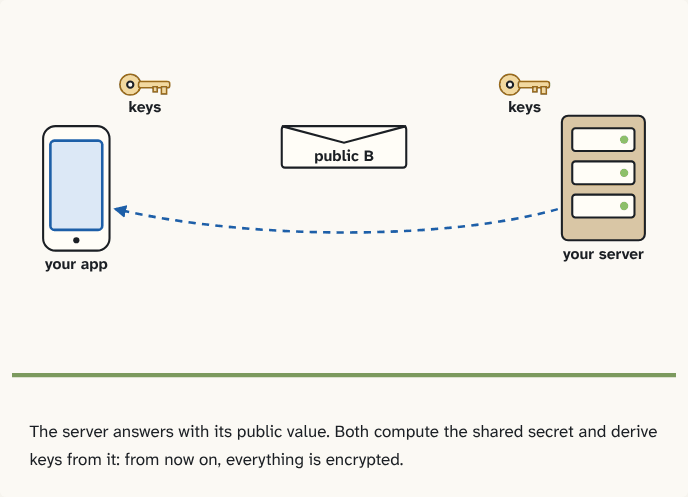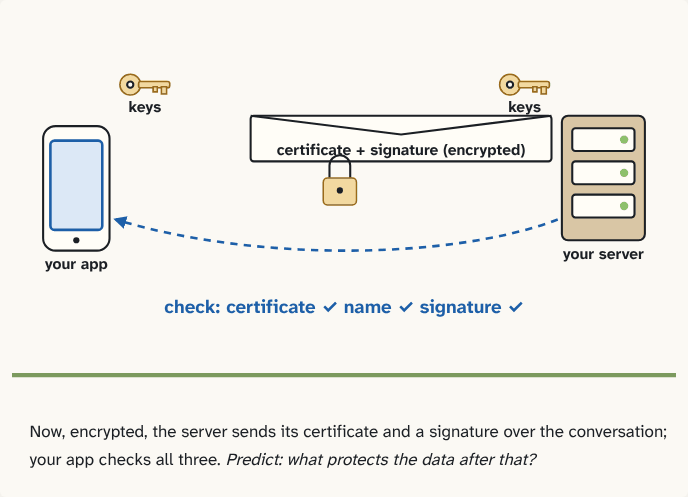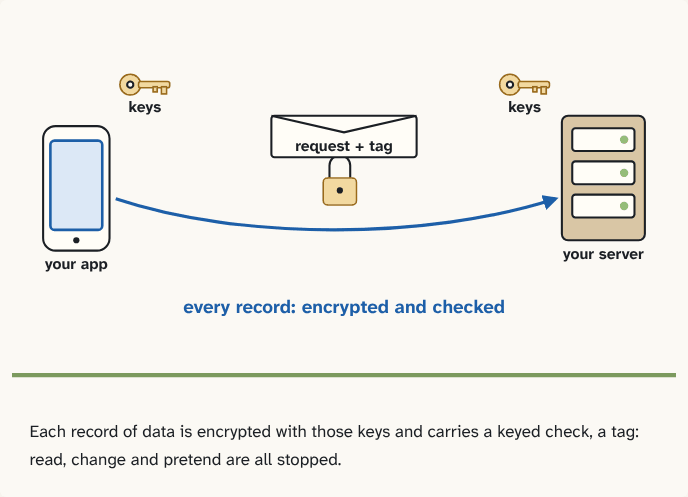
TLS, the S in HTTPS, starts with a short exchange: the handshake. Your app says hello and sends its public value (puzzle 3).
Step 1 of 4The server answers with its public value. Both compute the shared secret and derive keys from it: from now on, everything is encrypted.
Step 2 of 4Now, encrypted, the server sends its certificate and a signature over the conversation; your app checks all three. Predict: what protects the data after that?
Step 3 of 4Each record of data is encrypted with those keys and carries a MAC, its tag: read, change and pretend are all stopped.
Step 4 of 4
The building block
TLS is the protocol behind HTTPS: a set of agreed messages and rules. Before any of your data is sent, the app and the server have a short exchange: the handshake. In TLS 1.3 (the current version) it takes one round trip, there and back:
- Your app says hello and sends its public value for a key exchange (puzzle 3).
- The server answers with its own public value. Now both sides compute the shared secret, and from it they derive several keys (computed from it by a fixed recipe both sides follow): one set for the rest of the handshake, another for your data. From this point on, everything is encrypted.
- Still in the handshake, but now encrypted, the server sends its certificate (puzzle 7) and a signature over the whole conversation so far, made with its private key.
- Your app checks the certificate against the authorities it trusts, checks the name against the address, and checks the signature. A listener with a copied certificate fails here: it can't make that signature.
- Both sides end the handshake with a MAC (puzzle 6) over everything said so far, called Finished. Only now does each know that nobody changed the handshake on the way.
Then your data flows in records: chunks of data, each sent and checked on its own. Each record goes through one combined step, called authenticated encryption, for example AES in a mode built for it: it encrypts the record and attaches a MAC (puzzle 6), called a tag, both computed with keys derived from the shared secret. A listener who changes a byte can't make a matching tag, because it doesn't have the keys, so the change is detected and the record rejected. Reading: stopped by encryption. Changing: stopped by the tag on every record. Pretending: stopped by the certificate and the signature.
TLS doesn't hide everything: someone in the middle still sees which server you talk to and how much data goes back and forth. It hides what is said, and makes sure it's said to the right server.
The analogy
A courier and a bank: first the bank shows its registered seal and you both agree on a code, in plain sight but in a way no one listening can copy. Then every envelope goes out in that code, sealed so any tampering shows.
Check yourself
Sources
- RFC 8446: TLS 1.3 (the handshake "can be thought of as having three phases": Key Exchange, "Everything after this phase is encrypted", then Server Parameters and Authentication with Certificate and CertificateVerify; "all ciphers are modeled as Authenticated Encryption with Associated Data (AEAD)… a unified encryption and authentication operation"; "TLS does not hide the length of the data it transmits")
What you now know
A TLS handshake does a key exchange, has the server prove who it is with its certificate and a signature, and turns the shared secret into symmetric keys. Everything after that is encrypted with an AES-style cipher that also detects changes. Reading, changing and pretending are all stopped.
Answer every question above correctly to unlock the next puzzle.
That's everything published so far
You've reached the last puzzle of Encryption, from the ground up. Next: Module 2: Secrets on the phone, about where an app keeps keys and tokens: the Android Keystore and hardware-backed keys, encrypted storage, certificate pinning and when it backfires.
New puzzles are announced on LinkedIn and in the learning log feed.
Something wrong or unclear on this page? Tell me: a puzzle that didn't click is a bug in the puzzle.